


Hacking into Windows 7 Administrator Account Easily 08-24-2015, 09:44 AM
#1
Windows 7 Exploiting
Hi there SL. I just joined this forum and wanted to share a quick but useful tutorial that I made. Hope you enjoy, feel free to ask me anything.
Today, I will be telling you all about a vulnerability on Windows 7 Systems, and I will be teaching you how to use this vulnerability to bypass Login Screen, and grant admin access.
Lets go.
1-Accessing The Startup Repair Menu
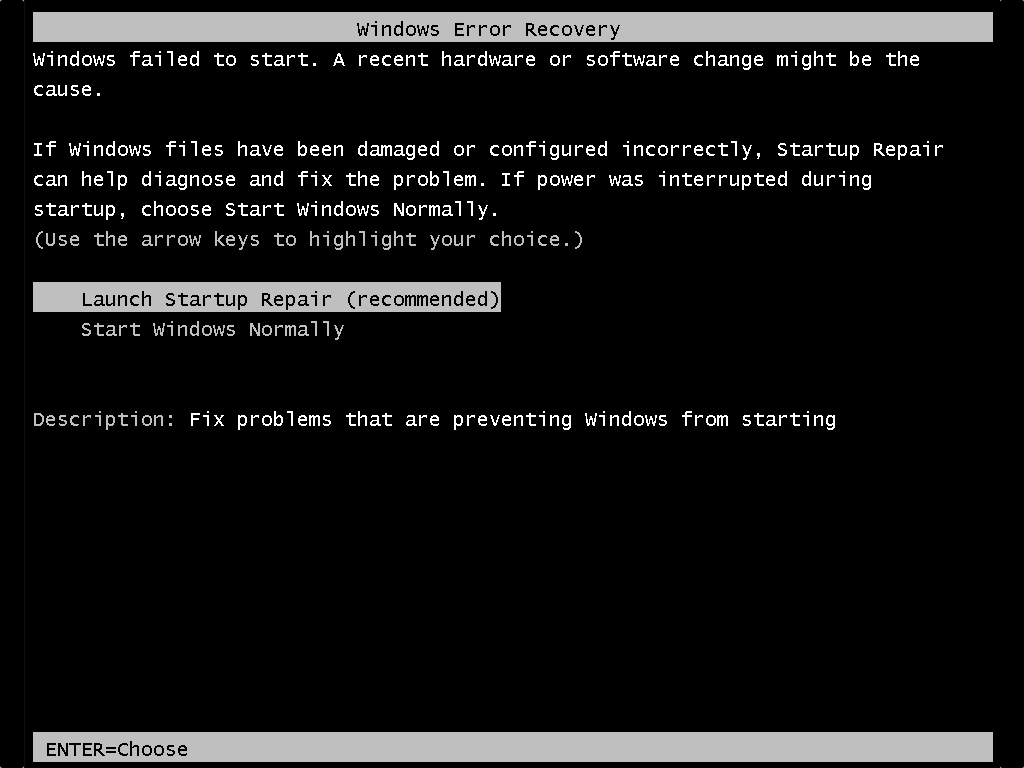
Alright, what we need to do on our tutorial is, we need to launch the startup repair menu on Windows 7. Force shutdown the computer by "shutdown –s –f" or by clicking on its button, and when the black background loading screen comes up, choose Launch Startup Repair. (if you can not see it there click CTRL+ALT+DELETE and repeat until it appears).
Alright, now let it load and wait a bit until a popup comes up saying "Do you want to restore your computer using System Restore?". Just click cancel and wait a little bit more.
Now another error should pop up saying "Startup repair cannot repair this computer automatically". That is a positive error, lol. Now click "View Details" and scroll down to the bottom and click the last linked-text. [X:\Windows\System32\en-US\erofflps.txt]

Notepad should pop up. Now we can exploit from notepad!
2-Accessing System32 From Notepad to Exploit
If you could came here without any problem, you are good to go. On notepad, go to File - Open. Now, change "files of type" to "all files" and lets explore a bit.
Go to Computer and then C:\Windows\system32. Scroll down a bit to find "cmd" and copy it.

Now scroll down to find "sethc" and rename "sethc" to "sethc1"

Okay now get to your "cmd copy" and rename it to "sethc".

to:

That's it! Good job.
3-Getting in the Admin Account
Alright, that's all of the necessary parts, done. Now lets have some fun. Reboot your computer, and on the login page click "L-Shift" 5 times. A cmd box with system32 privileges should pop up! You can do whatever you want now, lets open explorer.exe for example.
On the open cmd windows type in "explorer.exe" and windows bar should appear on login screen. Lets change admin pass now to login. On the cmd window, type in "net user". Users should appear... Now type in "net user Administrator *". It should ask for a new password now. Type in your password(it won't be seen). And activate the admin account, by typing "net user Administrator /active". Now you can login using account Administrator and your own password and have full access.
Alright, thats it for this simple tutorial guys. Hope I could helped, and if you have any questions you can ask them here.
Have Fun!
Hi there SL. I just joined this forum and wanted to share a quick but useful tutorial that I made. Hope you enjoy, feel free to ask me anything.
Today, I will be telling you all about a vulnerability on Windows 7 Systems, and I will be teaching you how to use this vulnerability to bypass Login Screen, and grant admin access.
Lets go.
1-Accessing The Startup Repair Menu
Alright, what we need to do on our tutorial is, we need to launch the startup repair menu on Windows 7. Force shutdown the computer by "shutdown –s –f" or by clicking on its button, and when the black background loading screen comes up, choose Launch Startup Repair. (if you can not see it there click CTRL+ALT+DELETE and repeat until it appears).
Spoiler:
Alright, now let it load and wait a bit until a popup comes up saying "Do you want to restore your computer using System Restore?". Just click cancel and wait a little bit more.
Now another error should pop up saying "Startup repair cannot repair this computer automatically". That is a positive error, lol. Now click "View Details" and scroll down to the bottom and click the last linked-text. [X:\Windows\System32\en-US\erofflps.txt]
Spoiler:
Notepad should pop up. Now we can exploit from notepad!
2-Accessing System32 From Notepad to Exploit
If you could came here without any problem, you are good to go. On notepad, go to File - Open. Now, change "files of type" to "all files" and lets explore a bit.
Go to Computer and then C:\Windows\system32. Scroll down a bit to find "cmd" and copy it.
Spoiler:
Now scroll down to find "sethc" and rename "sethc" to "sethc1"
Spoiler:
Okay now get to your "cmd copy" and rename it to "sethc".
Spoiler:
to:
Spoiler:
That's it! Good job.
3-Getting in the Admin Account
Alright, that's all of the necessary parts, done. Now lets have some fun. Reboot your computer, and on the login page click "L-Shift" 5 times. A cmd box with system32 privileges should pop up! You can do whatever you want now, lets open explorer.exe for example.
On the open cmd windows type in "explorer.exe" and windows bar should appear on login screen. Lets change admin pass now to login. On the cmd window, type in "net user". Users should appear... Now type in "net user Administrator *". It should ask for a new password now. Type in your password(it won't be seen). And activate the admin account, by typing "net user Administrator /active". Now you can login using account Administrator and your own password and have full access.
Alright, thats it for this simple tutorial guys. Hope I could helped, and if you have any questions you can ask them here.
Have Fun!