
+- Sinisterly (https://sinister.li)
+-- Forum: Hacking (https://sinister.li/Forum-Hacking)
+--- Forum: Hacking Tools (https://sinister.li/Forum-Hacking-Tools)
+--- Thread: Spaghetti - Web Application Security Scanner (/Thread-Spaghetti-Web-Application-Security-Scanner)
Spaghetti - Web Application Security Scanner - ZanGetsu - 09-16-2017
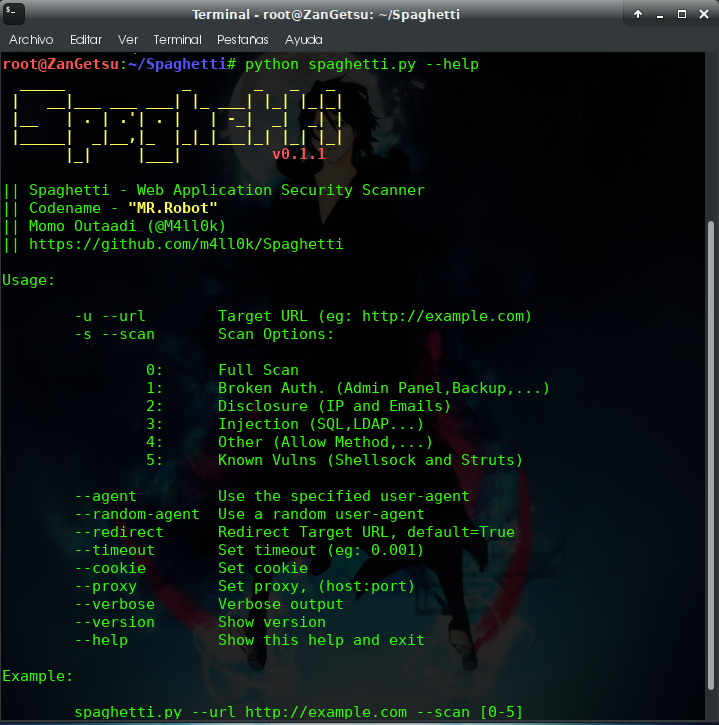
Fingerprints
- Server
- Web Frameworks (CakePHP,CherryPy,Django,...)
- Web Application Firewall (Waf) (Cloudflare,AWS,Barracuda,...)
- Content Management System (CMS) (Drupal,Joomla,Wordpress,Magento)
- Operating System (Linux,Unix,Windows,...)
- Language (PHP,Ruby,Python,ASP,...)
- Discovery:
- Apache
- Apache (mod_userdir)
- Apache (mod_status)
- Apache multiviews
- Apache xss
- Apache (mod_userdir)
- Broken Auth./Session Management
- Admin Panel
- Backdoors
- Backup Directory
- Backup File
- Common Directory
- Common File
- Log File
- Admin Panel
- Disclosure
- Emails
- IP
- Emails
- Injection
- HTML
- SQL
- LDAP
- XPath
- XSS
- RFI
- PHP Code
- HTML
- Other
- Allow Methods
- HTML Object
- Multiple Index
- Robots Paths
- Cookie Security
- Allow Methods
- Vulns
- ShellShock
- Struts-Shock
- ShellShock
- Apache
Example usage:
