
+- Sinisterly (https://sinister.li)
+-- Forum: General (https://sinister.li/Forum-General)
+--- Forum: The Lounge (https://sinister.li/Forum-The-Lounge)
+--- Thread: Windows Defender Is Getting Quick (/Thread-Windows-Defender-Is-Getting-Quick)
RE: Windows Defender Is Getting Quick - mothered - 10-24-2019
(10-23-2019, 09:57 PM)DedSpace Wrote:(10-19-2019, 09:33 PM)Strait McCool Wrote: So uhm, I guess it updated and it went ahead and quarantined the file again after I had restored it. Will this continuously happen? Should I just disable it at this point? It's getting annoying considering it's probably the program I use most on my PC.
It will turn back on after a while if you disable it:
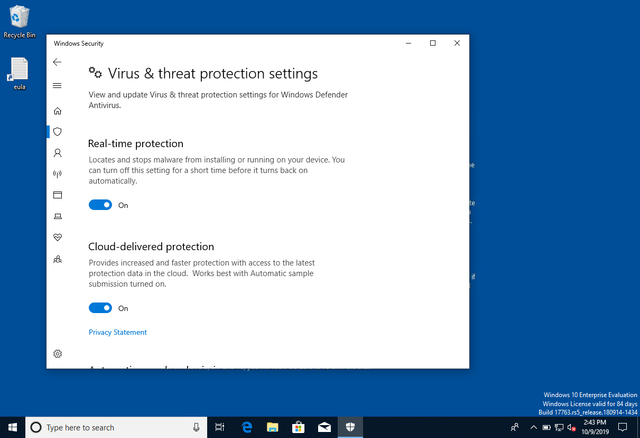
Not If It's disabled via the Group Policy Editor.
In terms of Windows 10, do note that the GPE Is only available In the Pro, Enterprise and Education editions.
RE: Windows Defender Is Getting Quick - ChristopherHALK - 11-02-2019
Well, it's their code after all. They can run whatever they want Biggrin
RE: Windows Defender Is Getting Quick - taban - 03-12-2020
(10-09-2019, 11:08 AM)DedSpace Wrote: I've been generating meterpreter reverse TCP payloads, hosting them on my LAN, downloading them on a MS Edge VM to run. Check that out if you don't know about it, it's very useful for things like this. The first couple of times, it worked like a charm. But now I get Windows Defender notifications, and it gets deleted before I can run it. It's worth noting that I'm generating a 64 bit payload in C encoded with 7 rounds of XOR, put into a template I wrote myself. Windows Defender went from being fine to being a pain in the space of an hour. Has anyone else experienced this, or did I get caught out by bad timing? Finally, is it worth biting the bullet and paying for a crypter?Hi
i purchased Data Encoder Crypter so it is working with common RATs and mostly get FUD resulted. it is bypass windows 10 defender