




Smooth-Sec. IDS / IPS system with Suricata motor and Snorby interface 09-23-2017, 09:34 PM
#1

Smooth-Sec is an IDS / IPS intrusion detection system whose engine is based on Suricata and with a Snorby web interface.
It is mounted on Linux UBUNTU 10.04 LTS. It comes from a system completely configured and ready to use. Created by Phillip Bailey.
the two main components of Smooth-Sec: Suricata and Snorby.
Suricata:
This is the IDS / IPS engine of The Open Information Security Foundation. It is Open Source and has some special features that make Suricata a very interesting engine. It is also fully compatible with the Snort and Emerging Threads rules.
We emphasize among the characteristics of Suricata:
Multi-Threaded Processing. One of the most important characteristics of Suricata that allows the execution of several processes / subprocesses simultaneously. We can then assign the number of threads per CPU / Cores and what threads. In this way it is able, among other things, to process a large number of packages simultaneously increasing performance.
Automatic Protocol Detection. Apart from the protocols IP, TCP, UDP and ICMP, Suricata has keywords for other protocols such as FTP, HTTP, TLS, SMB. That way we can write rules regardless of the port that a protocol uses, either by default or not as it is automatically detected.
Performance Statistics. Statistics and performance analysis. These statistics are rolled into /var/log/suricata/stat.log.
HTTP Log Module. Suricata, regardless of alerts, dumps all HTTP requests (either from HOME_NET> EXTERNAl_NET or in the opposite direction) into a /var/log/http.log file. Logging of these requests is stored in Log Apache format.
Gzip decompression by the HTTP parser.
Supports, like Snort, Unified2 Output.
Supports IPv6.
Snorby:
Snorby is a web front-end for sensor-based IDS / IPS alert management. In the case of Smooth-Sec based Suricata motor. Its graphical interface is very simple with a wide and intuitive view of the display of alerts.
In summary, with Snorby we can have a quick view of the alerts generated by the different suricata sensors through an intuitive and attractive interface.
The version used by Snorby's Smooth-Sec is 2.2.5
Smooth-Sec installation.
Download the .iso from here: https://sourceforge.net/projects/smoothsec/
We install a physical machine or through VMWare.
Once we start with the .iso:
- we use the install to hard disk option.
- installation is very simple and includes the normal operations of a Debian / Ubuntu installation, such as configuring partitions, guided or not, GRUB, etc.
- once the installation is done we restart.
- we indicate password for the root account.
- we follow the indications of the installation.
- configure the network interface.
- we reinitiate.
- a screen tells us, based on the configured IP, the out of accessing the Snorby web interface via https (02).
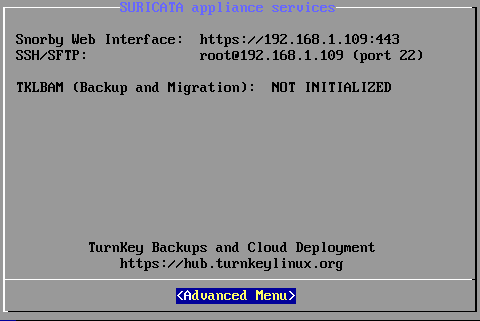
In this same screen: Advanced Menu> Quit, we can access command line for the advanced configuration of Smooth-Sec.
we access through https: // IP: 443 / and we are asked for username and password that will be: snorby@snorby.org / snorby.
Smooth-Sec running.
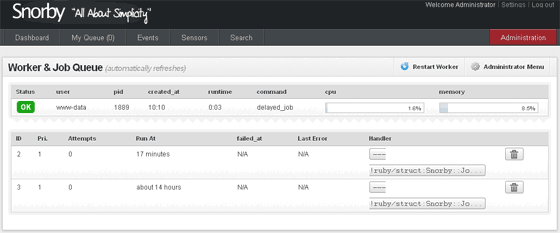
From the Dashboard or Snorby main screen> Administration (top right in red)> Administrator menu> Worker & JoB Queue, we see that everything is correct and working:
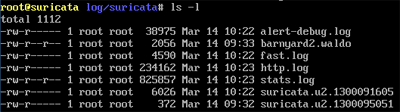
We see that the alert files are also being generated in / var / log / meerkat as well as the unified2 format for Snorby:
source: dadaweb.com


