


IronSquirrel - Encrypted Browser Exploits Delivery 10-03-2017, 01:47 AM
#1
IronSquirrel - Encrypted Browser Exploits Delivery
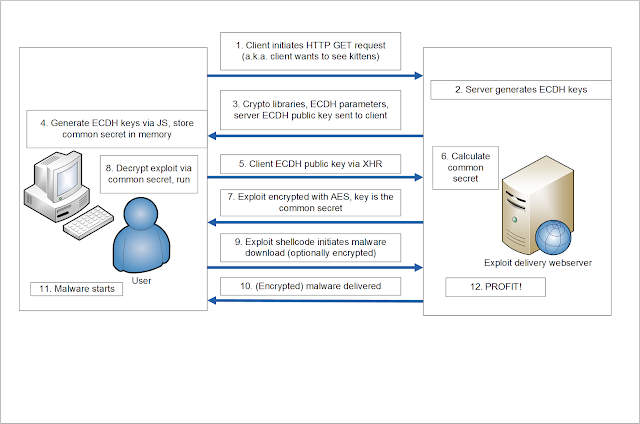
Ironsquirrel project aims at delivering browser exploits to the victim browser in an encrypted fashion. Ellyptic-curve Diffie-Hellman (secp256k1) is used for key agreement and AES is used for encryption.
By delivering the exploit code (and shellcode) to the victim in an encrypted way, the attack can not be replayed. Meanwhile the HTML/JS source is encrypted thus reverse engineering the exploit is significantly harder.
By delivering the exploit code (and shellcode) to the victim in an encrypted way, the attack can not be replayed. Meanwhile the HTML/JS source is encrypted thus reverse engineering the exploit is significantly harder.
Prerequisites
Mandatory dependencies - clone the IRONSQUIRREL project, cd into the project directory, and run the following commands:
sudo apt-get install ruby-dev
bundle install
Actually nokogiri and gibberish gems will be installed.
Optional dependency (for Powershell based environment aware encrypted payload delivery): Ebowla https://github.com/Genetic-Malware/Ebowla
Installing
Clone the IRONSQUIRREL project
Install the prerequisites
(Optional) Edit IRONSQUIRREL.rb
Change the listen port
If Ebowla is used, configure the paths
(Optional) If Ebowla is used, configure genetic.config.ecdh in the Ebowla install directory
Run IRONSQUIRREL.rb

Usage
Code:
git clone https://github.com/MRGEffitas/Ironsquirrel && cd Ironsquirrel
bundle install
cd public
sudo cp *.* /var/www/html/
ruby IRONSQUIRREL.rb --exploit full_path_to_exploit
Locked.







